Modular SaaS application foundation
Platform Architecture & Engineering
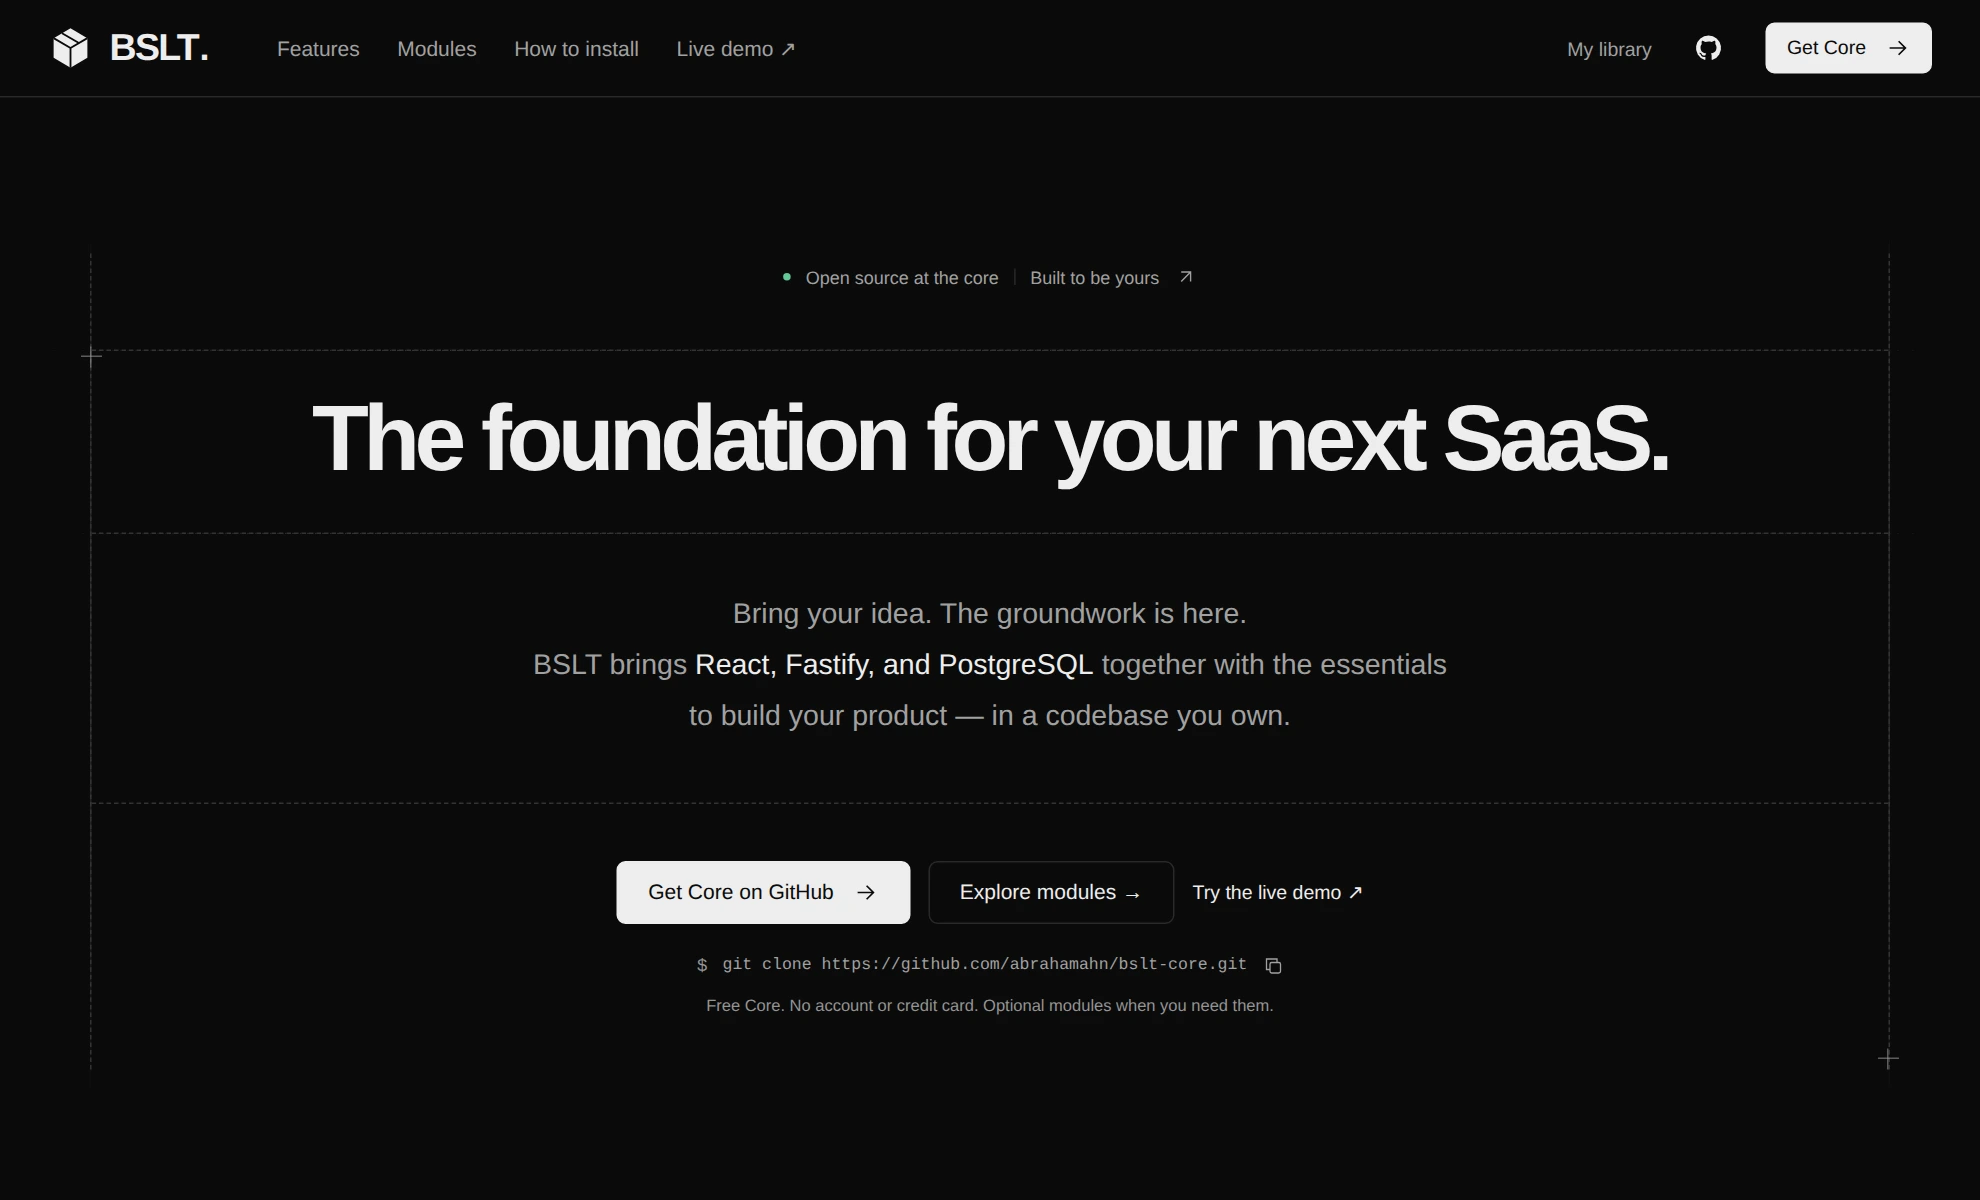
Reusable SaaS core with authentication, RBAC, append-only audit logs, and CI gates.
Sole platform author maintaining the React/Fastify/PostgreSQL starter, auth-core integration, migration runner, and conformance tests.
Deployed live at bslt.dev and used as the foundation layer for client portals and full-stack SaaS builds.
Engineering & product case study
Problem & workflow context
Spinning up new client SaaS apps repeatedly risked subtle bugs in session rotation, password/step-up policy, migration drift, and security audit logging when rebuilt under tight project deadlines.
Decision & rejected alternative
Extracted pure authentication/session policy into zero-I/O conformance-tested modules (auth-core) and kept the web starter to a single clone-and-own React + Fastify + PostgreSQL codebase with explicit SQL migrations. Rejected heavy microservice templates and ORM magic that obscured query plans and transaction boundaries.
Failure encountered & diagnosis
Concurrent token-refresh requests from multiple browser tabs initially caused false reuse lockouts during network jitter. Diagnosed via deterministic session-epoch conformance fixtures and introduced bounded grace-window rotation with explicit credential-epoch binding.
Verification, role & current status
Verified with language-neutral JSON conformance vectors shared across TypeScript and Rust, isolated PostgreSQL migration-drift tests, and end-to-end Playwright auth/session flows.
Architecture & reproducible evidence
- Deterministic session lifetime, refresh rotation, lockout, and secret-safe audit event contracts.
- Ordered SQL migration runner that refuses accidental execution against non-test databases during verification.
- Powers production client portals with zero third-party auth vendor lock-in.
Technology stack
See all 9 roles, Penn M.A.S. status, U.S. citizenship/relocation logistics, and printable résumé on one page.
Open Recruiter View & Public Résumé →